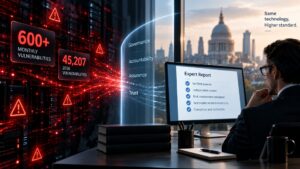
The volume of software vulnerabilities discovered by AI systems has surged past every historical benchmark. Microsoft patched over 600 vulnerabilities in a single month in July 2026, while the US National Vulnerabilities Database recorded 45,207 flaws in the first seven months of 2026 alone, approaching the full-year total for 2025. The AI governance gap this creates for regulated professionals who rely on AI-assisted tools is growing faster than the cybersecurity industry can close it.
Billions of dollars in venture capital are flowing into defensive security tooling, but almost none of it addresses the accountability question that matters most to expert witnesses, dispute lawyers, and other regulated professionals: when the AI tool you relied on sits on a compromised platform, who is responsible for the work product it helped you produce?
Why are AI-discovered vulnerabilities accelerating so fast?
The acceleration is structural, not cyclical. Frontier AI models can now scan codebases and identify exploitable flaws at a pace no human team can match. Anthropic’s Claude Mythos Preview identified over 6,200 high or critical severity vulnerabilities in foundational open-source software during early testing, of which only 97 had been addressed as of May 2026. At Black Hat USA 2026, researchers demonstrated that integrating AI workflows into vulnerability scanning produced roughly 600 new discoveries from a single research team, with the constraint being not detection capability but the speed at which findings could be responsibly disclosed.
The numbers at the industry level tell the same story. Oracle patched 1,449 security vulnerabilities in its July 2026 update, an all-time record for the company and nearly five times its figure for the same period in 2025. Microsoft’s August 2026 Patch Tuesday addressed over 400 issues, a volume the company described as approximately five times its pre-AI monthly average. Ecsper’s governance pillars exist precisely because this environment demands infrastructure-level accountability, not post-hoc assurance.
Why is the cybersecurity response not enough for regulated professionals?
The venture capital response to this surge has been rapid and large. AI-native security operations centres, agent security layers, and infrastructure hardening tools are attracting significant funding. That investment addresses the right problem at the wrong layer for regulated professionals.
Cybersecurity tools protect systems. They do not protect professional accountability. A security operations platform can detect and patch a vulnerability in a cloud service. It cannot tell a tribunal whether the expert report drafted with an AI assistant on that platform was produced under adequate governance, reviewed by a qualified professional, and supported by a defensible audit trail. For an expert witness operating under CPR Part 35, or a solicitor under SRA supervision requirements, the security of the underlying infrastructure is necessary but not sufficient.
The governance gap sits between the infrastructure layer (where defensive investment is concentrated) and the professional output layer (where accountability is determined). According to a 2026 Compliance Week survey, 83% of organisations are using AI tools, but only 25% have implemented a governance framework strong enough to manage them. A separate analysis found that 43% of companies have no AI usage policy at all.
What does the vulnerability surge mean for professional work products?
Every AI-assisted document, report, or analysis produced by a regulated professional now sits on a technology stack whose attack surface is expanding at an unprecedented rate. This creates three specific risks that infrastructure security alone cannot address.
First, provenance becomes harder to guarantee. When the platform your AI assistant runs on is patching hundreds of vulnerabilities per month, the chain of custody for any AI-assisted work product depends on whether your governance infrastructure can demonstrate which model version, which data boundaries, and which human review process applied at the point the work was produced.
Second, the standard of care is rising. Regulators are moving from principle to enforcement. The EU AI Act reaches full enforcement for high-risk AI systems in August 2026, with penalties of up to 35 million euros or 7% of global annual revenue. In the UK, the SRA’s August 2026 Warning Notice confirmed that law firms face disciplinary action for using AI without documented oversight. Professionals who cannot demonstrate governance over their AI-assisted work products face regulatory exposure regardless of whether the underlying infrastructure was secure.
Third, the disclosure burden is compounding. When vulnerabilities are discovered and patched at this rate, every organisation using AI tools must be able to answer a new question: were any of your AI-assisted outputs produced during a window when a now-patched vulnerability was present? Without a defensible record, the question is unanswerable.
Who carries the accountability when AI infrastructure is compromised?
The accountability sits where it has always sat: with the professional who signs the work. The difference is that AI has made the gap between the professional’s signature and the technology stack beneath it vastly wider and harder to bridge without purpose-built governance infrastructure.
No amount of defensive security tooling changes who is accountable for the professional output. A vulnerability scanner protects the platform. A governance layer protects the professional. The two are complementary, but the market is investing almost exclusively in the former while the latter remains largely unaddressed.
This is the accountability gap that the AI Assurance Forum will examine at its inaugural panel on 14 October 2026 at DWF, 20 Fenchurch Street, London. The panel, “The Accountability Gap in AI-Assisted Professional Practice”, brings together practitioners, regulators, and technologists to address a question the cybersecurity investment boom has left unanswered: when AI-assisted professional work goes wrong, who is responsible, and what evidence do they need to defend that responsibility?
What should regulated professionals do now?
Start with three steps. First, check your governance exposure in three minutes. Understand whether your current AI usage is documented, governed, and auditable. Second, separate your infrastructure security from your professional governance. Your cloud provider’s security certifications protect their systems, not your professional standing. Third, ensure every AI-assisted output produced under your name has a defensible record: which model, which boundaries, which human reviewer, which version of the facts.
The vulnerability surge is not a cybersecurity problem that regulated professionals can outsource. It is a governance problem that sits at the intersection of technology risk and professional accountability, and it requires infrastructure built for that intersection.
See the full tracker: over 2,000 documented cases of AI misuse in court proceedings. Ecsper AI Risk Intelligence